k3s Disk Usage: 9 Steps to Find and Clean Unused Images
A real k3s disk audit that found stale container images, recovered about 28 GB across three workers, and tuned kubelet garbage collection safely.
A real k3s disk audit that found stale container images, recovered about 28 GB across three workers, and tuned kubelet garbage collection safely.
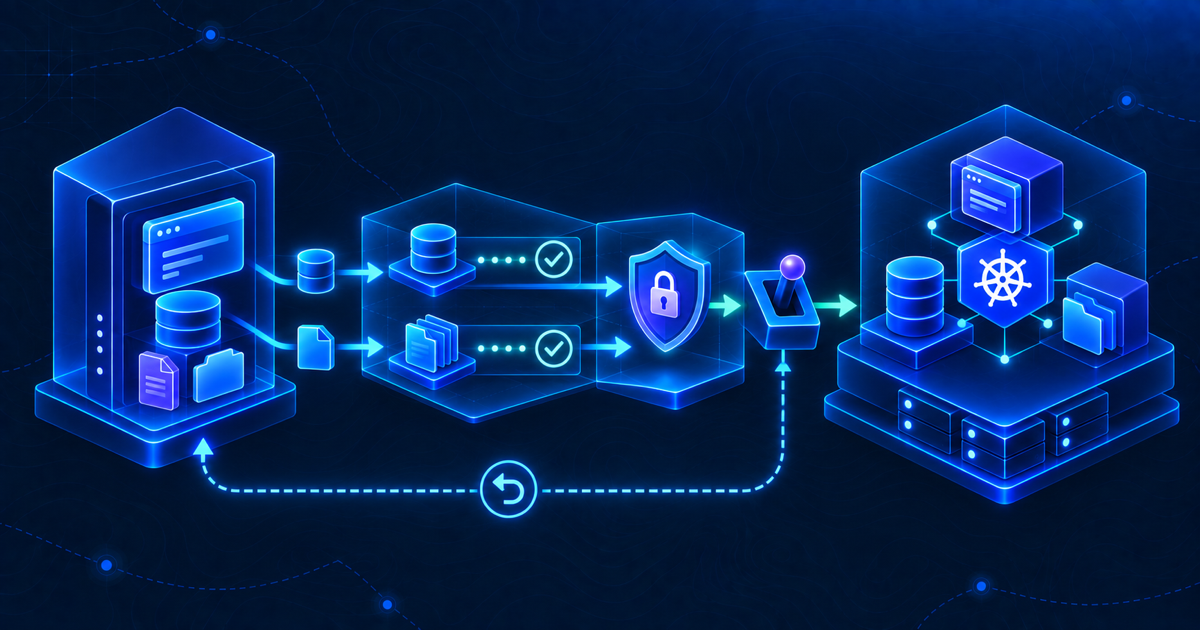
A practical, evidence-based VM-to-k3s migration checklist from a real Snipe-IT cutover: independent backups, data verification, NFS writes, TLS testing, DNS change and rollback.
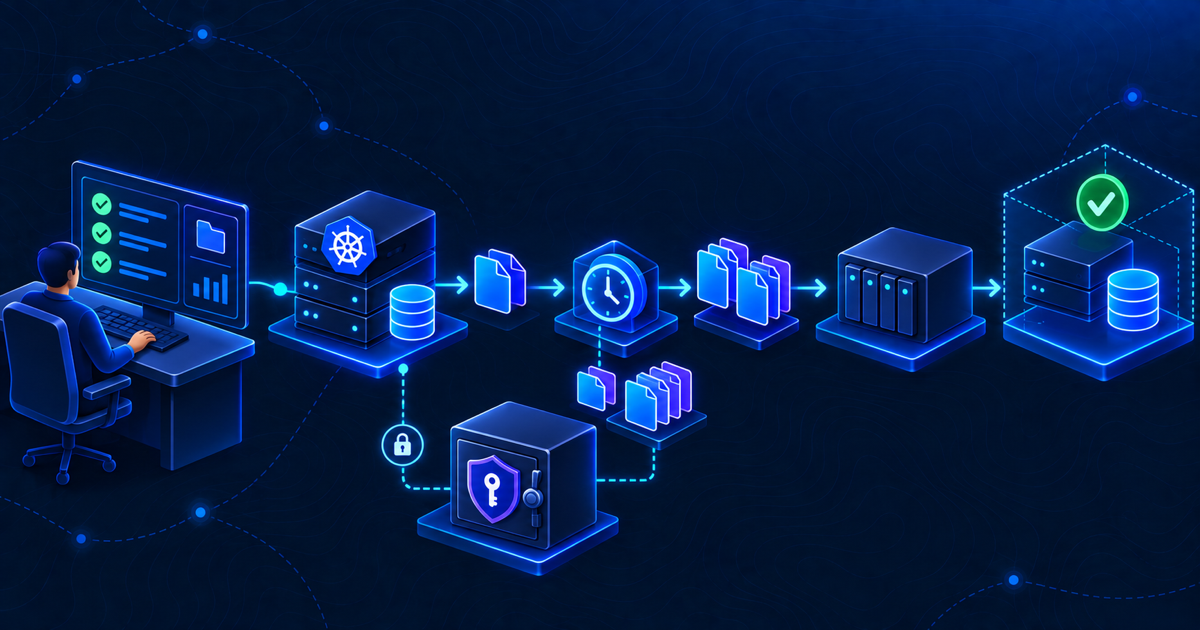
A non-destructive k3s backup audit covering datastore type, snapshot inventory, schedule, retention, QNAP copies, server-token protection, file integrity and an isolated restore test.
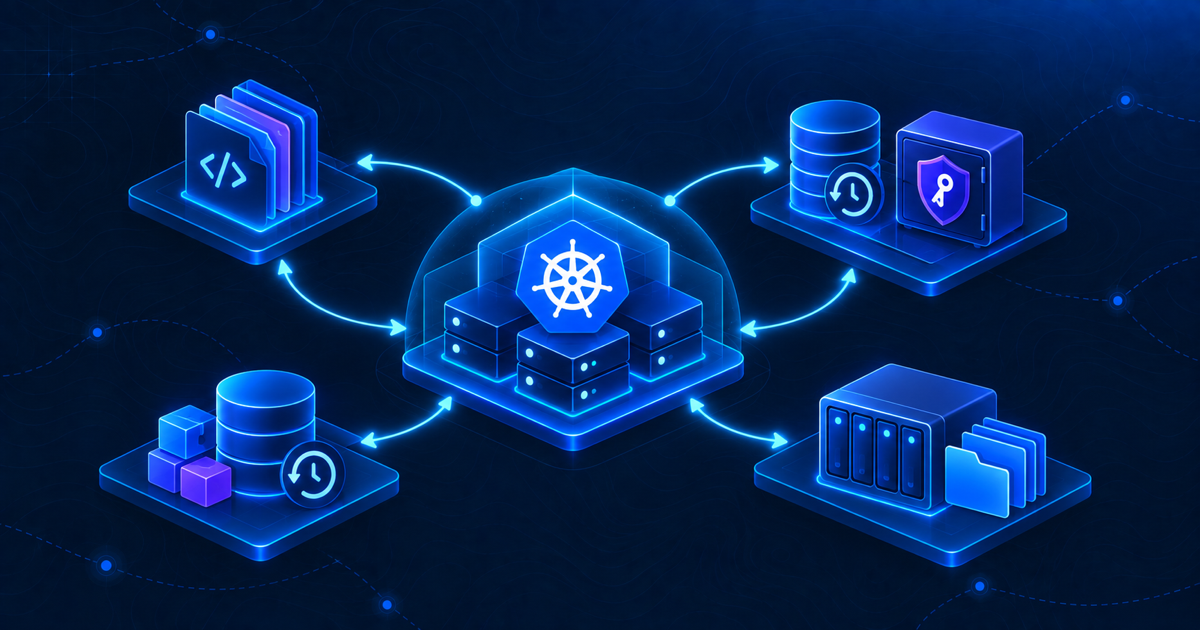
A field note from a small k3s environment: etcd snapshots matter, but credible recovery also needs the original server token, GitOps state, database backups, persistent file protection and restore evidence.
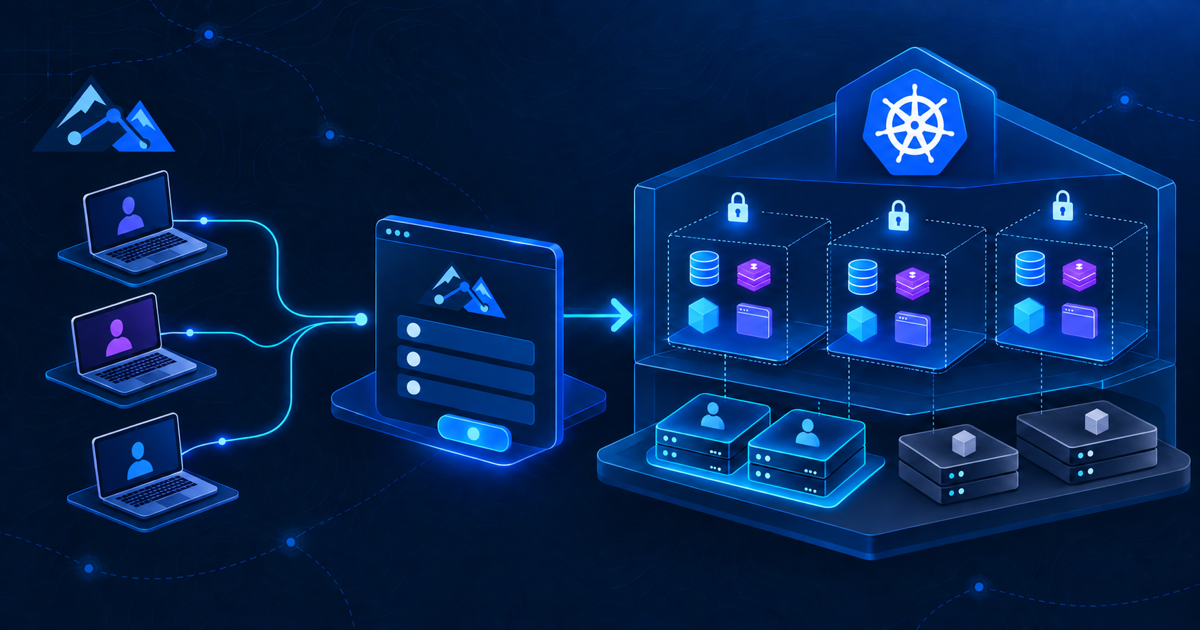
A practical design note for building a resource-constrained Kubernetes developer platform on an existing k3s cluster with Rancher, isolated namespaces, quotas, dedicated workers and automatic cleanup.
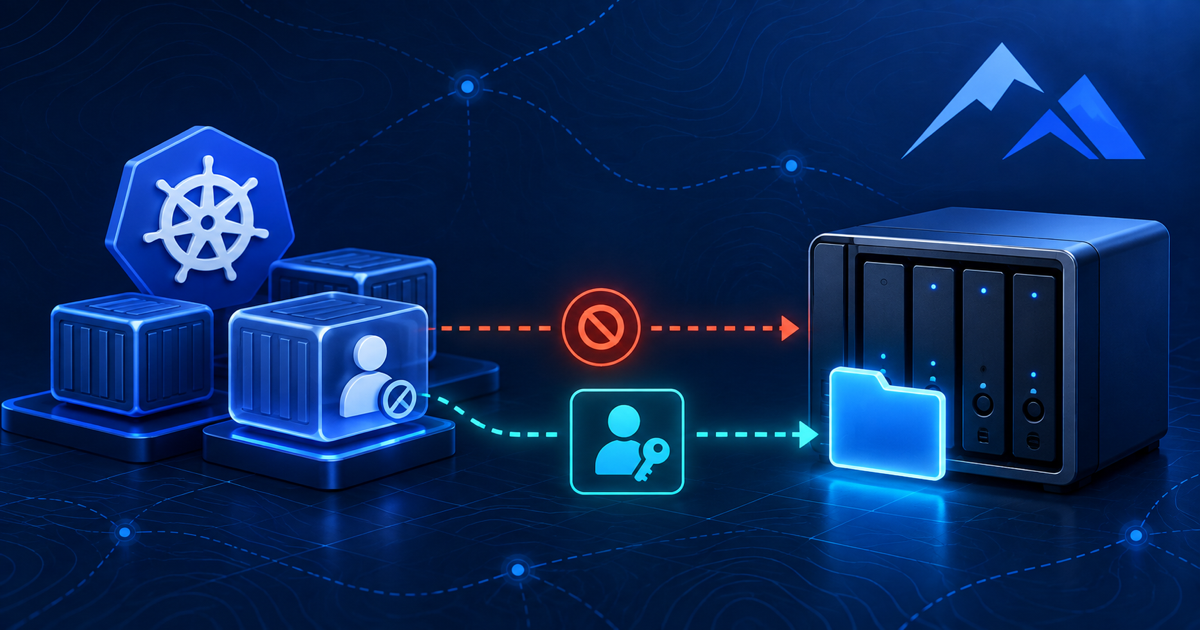
A real troubleshooting sequence for QNAP-backed Kubernetes storage when root can write to an NFS PVC but the non-root application user receives Permission denied.
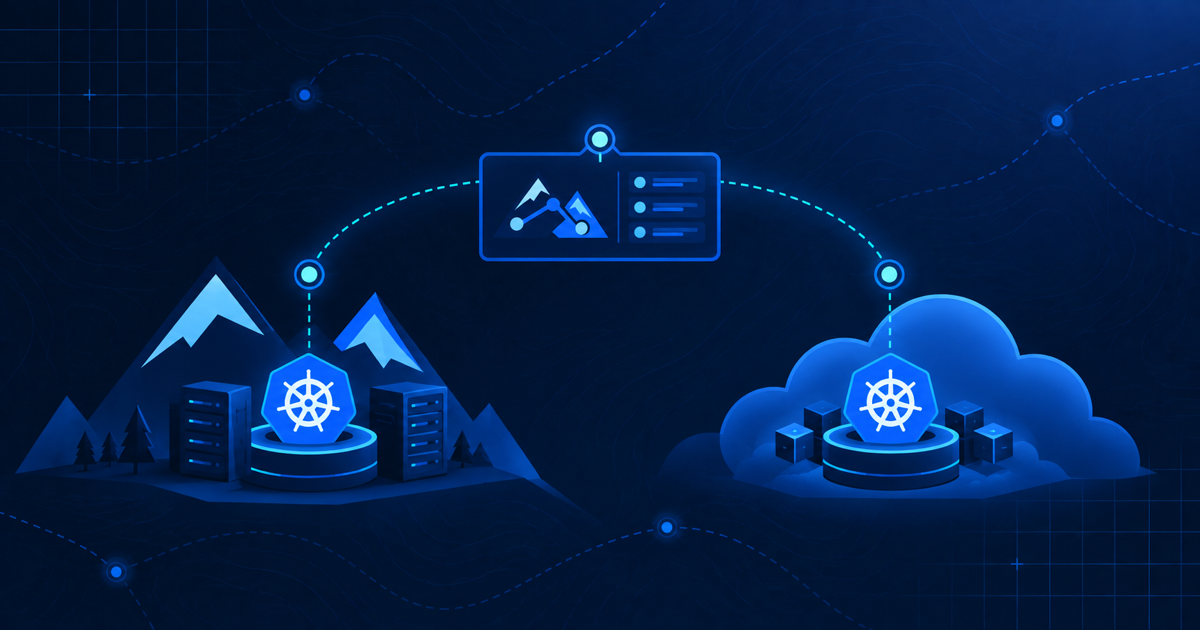
A practical architecture decision: Azure Arc for the existing k3s cluster, a stretched cluster, or separate on-premises k3s and Azure AKS.
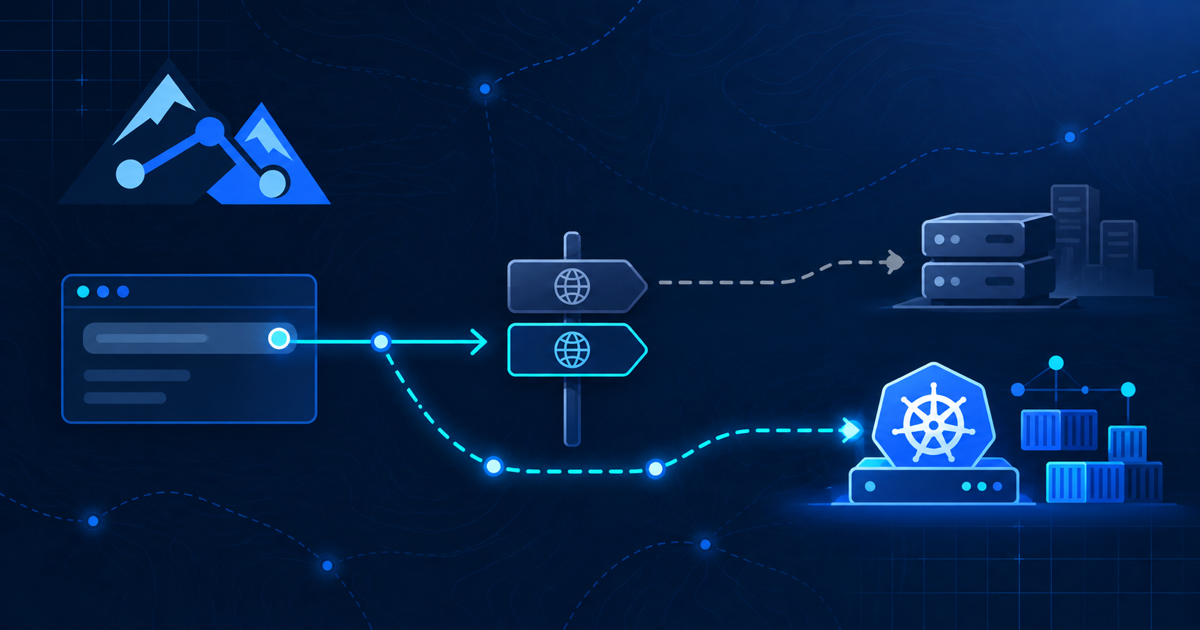
Use curl –resolve to test Kubernetes Ingress routing, TLS, redirects and application assets against a new IP before changing public DNS.
This k3s migration inventory produced seven practical rules for deciding what belongs in Kubernetes, what stays on a VM and what should be retired.
Four worker nodes looked redundant until I mapped them back to the single Proxmox host underneath. This is the HA redesign before more workloads move to k3s.